

OWASP WSTGWeb Security Testing Guide
Web application and API testing
- Web application
- Standalone API
Manual, business-logic-first penetration testing by a named researcher, not a scanner report with a consultancy logo on the front. Scoped, tested and delivered inside one week.
Independent offensive securityBased in Belgium
CriticalCWE-89WSTG-INPV-05
Why teams choose The XSS Rat
The usual pentest: “Scanner output, lightly edited, delivered as the report.”
The XSS Rat: Every finding exploited by hand before it is reported.
Automated tooling runs in the background for coverage. Every reported finding is manually verified and manually exploited; no unvalidated scanner output ever reaches your report.
Automated tooling runs in the background for coverage. Every reported finding is manually verified and manually exploited; no unvalidated scanner output ever reaches your report.
The usual pentest: “Sold by one person, tested by whoever is on the bench that week.”
The XSS Rat: One named researcher scopes it, tests it and writes it.
The person who scopes the engagement is the person who tests it and writes the report — a named researcher with accepted findings at OpenAI and Google, not a rotating bench.
The person who scopes the engagement is the person who tests it and writes the report — a named researcher with accepted findings at OpenAI and Google, not a rotating bench.
The usual pentest: “A list of what broke, and nothing on what was checked and held.”
The XSS Rat: A record of what was tested and held, not just what broke.
Testing follows OWASP's published guides, so the coverage record shows exactly what was tested and found clean, not just what was found broken.
Testing follows OWASP's published guides, so the coverage record shows exactly what was tested and found clean, not just what was found broken.
The usual pentest: “A severity label and a link to a generic advisory.”
The XSS Rat: Repro steps, a CVSS 4.0 score, the impact and the fix.
Each finding ships with reproduction steps a developer can follow, a CVSS 4.0 score, the business impact in plain language and a concrete fix.
Each finding ships with reproduction steps a developer can follow, a CVSS 4.0 score, the business impact in plain language and a concrete fix.
The usual pentest: “Billed by the hour, so the bill grows with the target.”
The XSS Rat: Fixed price, fixed date, never longer than a week.
Fixed price, fixed date, published day rate. No engagement runs longer than one week; a bigger target becomes two scoped engagements, never an open-ended bill.
Fixed price, fixed date, published day rate. No engagement runs longer than one week; a bigger target becomes two scoped engagements, never an open-ended bill.
The usual pentest: “A checklist run at the login page; the logic flaws go untested.”
The XSS Rat: Business logic and authorisation first, like an attacker.
The same attacker mindset that lands bugs in real bounty programmes is pointed at your application — business logic and authorisation first, because that is where the findings that matter live.
The same attacker mindset that lands bugs in real bounty programmes is pointed at your application — business logic and authorisation first, because that is where the findings that matter live.
What I test
Every engagement is fixed-price, fixed-date, and finished inside one week. You know the cost and the calendar before anything starts.
4 of 5 days in the week.
Authenticated, multi-role testing of the whole application, front end and the backend behind it — not a scanner report with a logo on it. Broken access control and business-logic abuse are where I spend most of the engagement, because that is where the findings that matter actually live.
Backend included
The backend endpoints this application actually calls are inside the engagement — the API surface behind the flows, roles and authorisation being tested. You do not add a separate API engagement to cover that.
What it covers
Backend included
The backend endpoints this application actually calls are inside the engagement — the API surface behind the flows, roles and authorisation being tested. You do not add a separate API engagement to cover that.
What it covers
3 of 5 days in the week.
For when the API is the product, not the plumbing behind a front end. REST, GraphQL and gRPC, tested against the spec and then well beyond it. APIs fail on authorisation far more often than on injection, so every endpoint is exercised across every role — including the ones your documentation does not mention.
When to pick this
For when the API itself is the target: API-first products, public or partner APIs, large endpoint sets, and functionality no front end exercises. Not an automatic add-on to a web or mobile test.
What it covers
When to pick this
For when the API itself is the target: API-first products, public or partner APIs, large endpoint sets, and functionality no front end exercises. Not an automatic add-on to a web or mobile test.
What it covers
5 of 5 days in the week.
iOS and Android, tested on real devices. Static review of the binary, dynamic instrumentation at runtime, and the backend the app talks to, to the depth the app’s own flows require — because a mobile app is mostly an API client wearing a nice interface. A single platform takes less; both fit inside the week.
Backend included
The backend endpoints this application actually calls are inside the engagement — the API surface behind the flows, roles and authorisation being tested. You do not add a separate API engagement to cover that.
What it covers
Backend included
The backend endpoints this application actually calls are inside the engagement — the API surface behind the flows, roles and authorisation being tested. You do not add a separate API engagement to cover that.
What it covers
How to read the figures
A quoted day is a day of engagement, not a day at the keyboard: testing, analysis, the written report and the delivery debrief for that scope all sit inside the number you approve. Each figure is one full engagement on that surface at standard depth, multi-role and authenticated. These are the same engagements the Professional package buys, at the same prices — the packages differ by depth and deliverables, not by surface. See the packages.
Who does the work
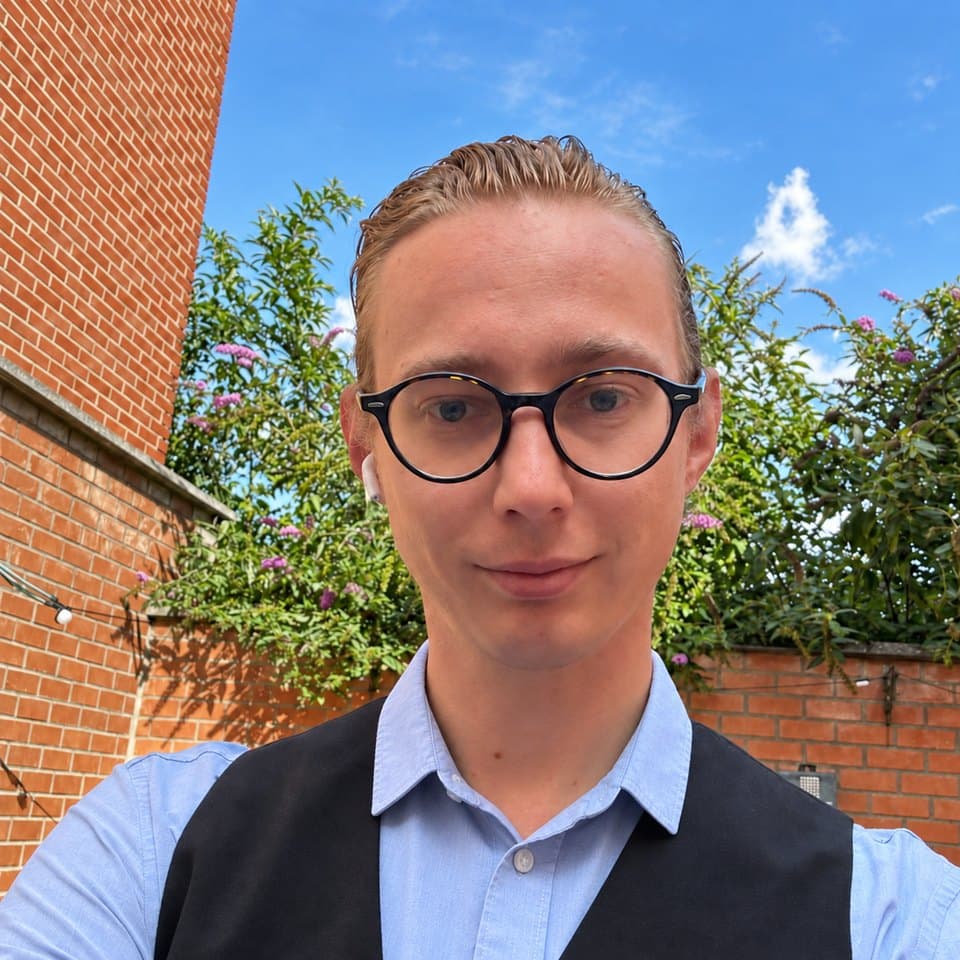
Wesley Thijs
Independent penetration tester and security researcher
I test web applications, APIs and mobile apps by hand, business logic first, and I write the report myself. The findings that matter — broken access control, tenant isolation, workflow abuse — are not the ones a scanner finds, so that is where the engagement time goes.
The method is the one I codified into three professional certifications and have taught for more than seven years. The hunters I coach have landed first triages at Google, P3s at OpenAI, and the largest payout a programme had ever made. Your engagement gets the same method, from the person who wrote it.
How it runs
The same process every time, whether it is a three-day API review or a full mobile engagement — structured on PTES, tested to OWASP's guides.
A 45-minute call to agree targets, roles, test accounts, out-of-scope systems and a testing window. You get a fixed price and a fixed date before anything starts — no hourly surprises. A 30% deposit on signature holds the dates.
Human-led. Tool-assisted.
Automated tooling runs in the background for coverage and occasionally catches something. It never writes the report.
 Objection: Mobile runtime exploration and pinning bypass
Coverage & standards
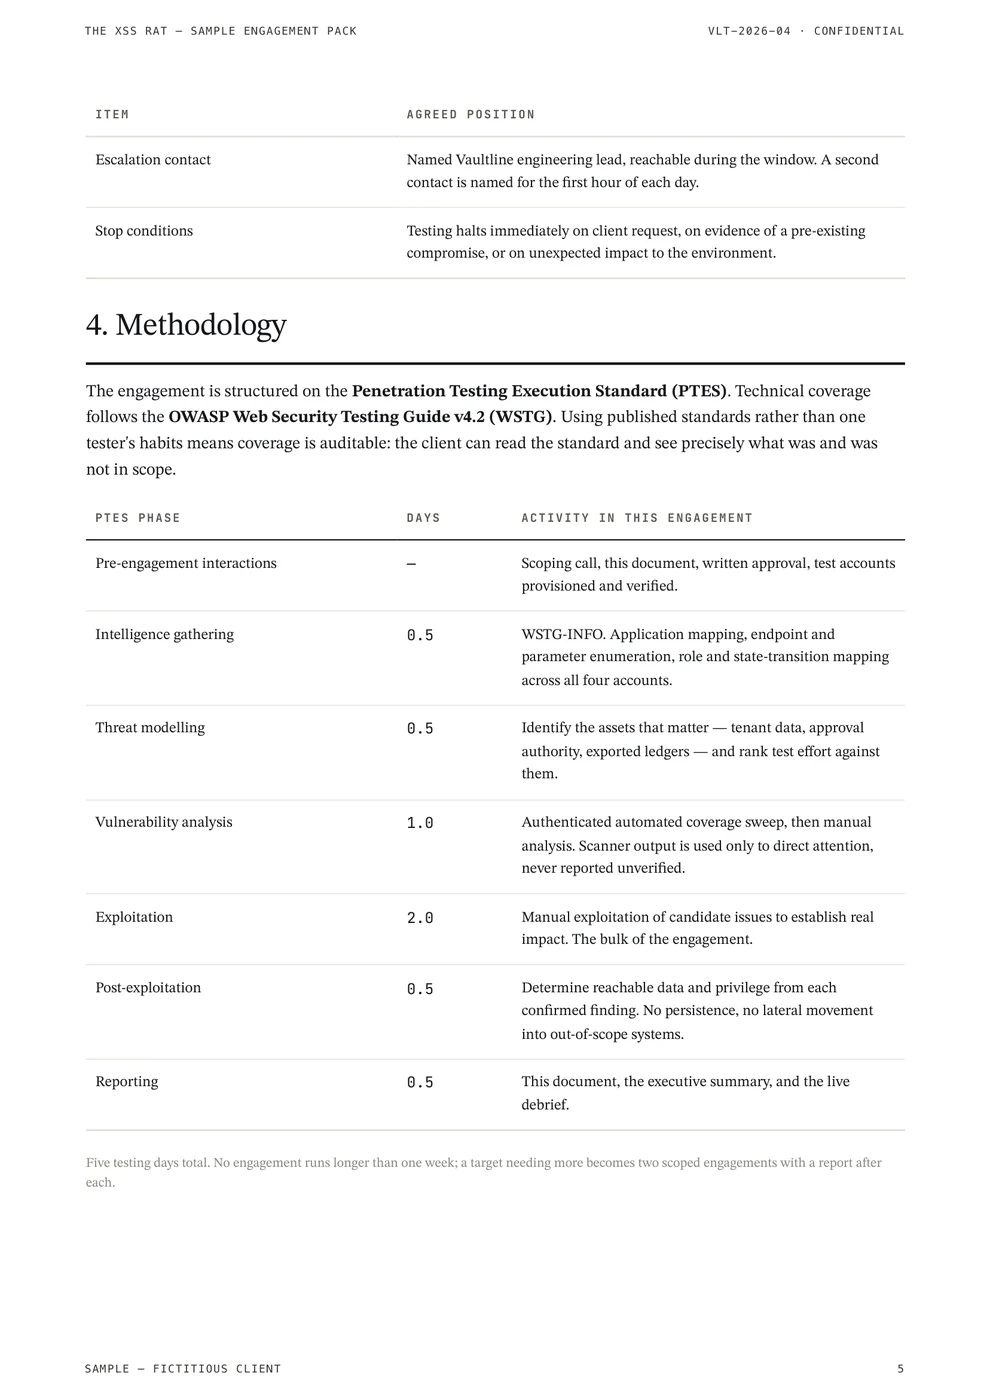
You can read the standard and see exactly what was in scope. The engagement is structured on PTES; the testing itself follows OWASP's Web and Mobile Security Testing Guides.
PTESPenetration Testing Execution Standard
Engagement structure, end to end
OWASP WSTGWeb Security Testing Guide
Web application and API testing
OWASP MASTGMobile Application Security Testing Guide
iOS and Android testing
See it before you buy it
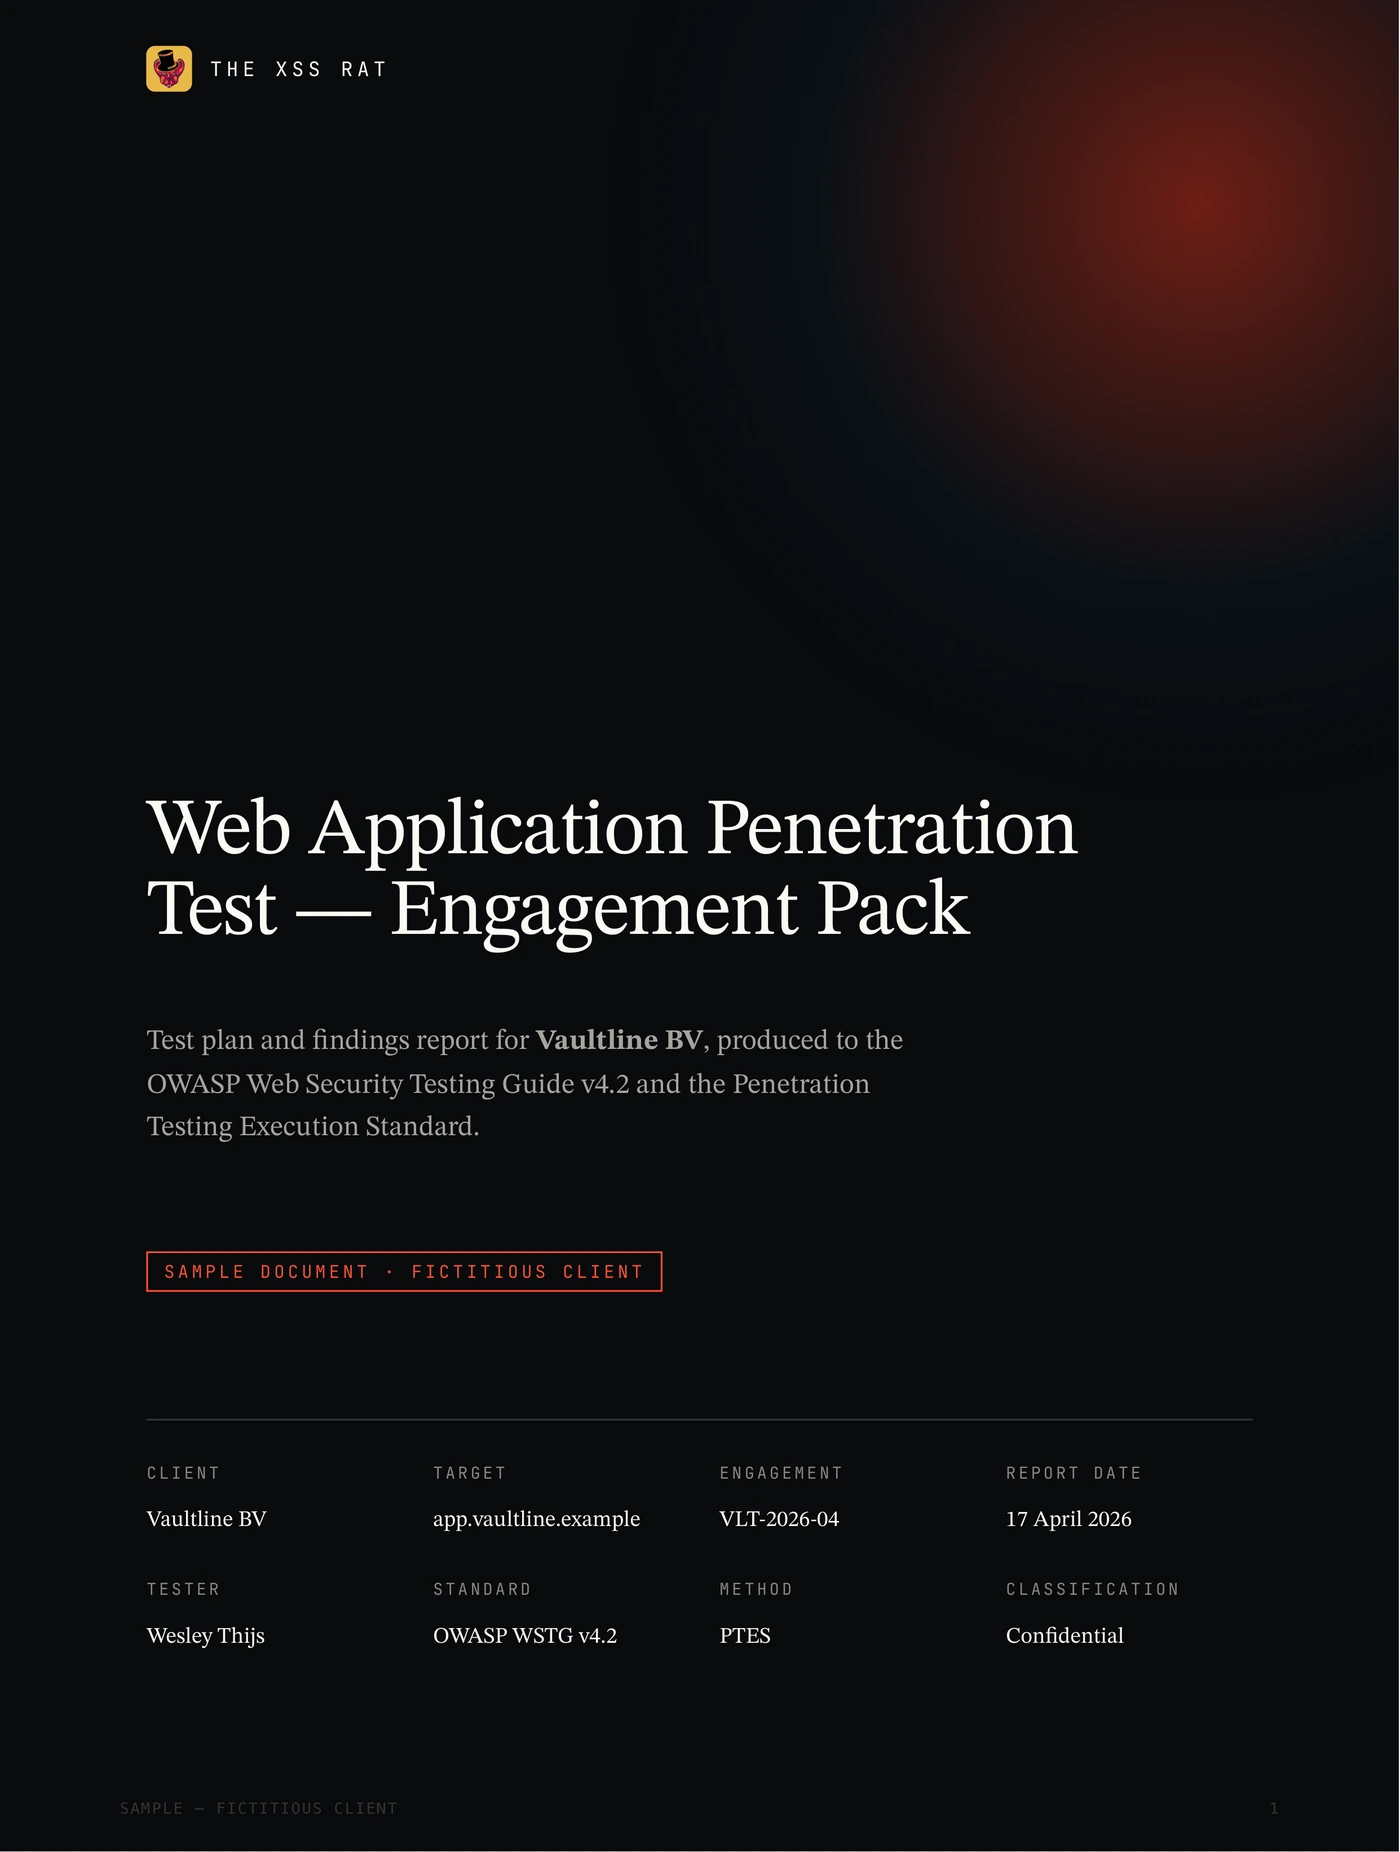
Every engagement ends in the same document set. The complete sample pack below is what a client receives — built around a fictitious client so nothing real is disclosed.
Contents
Track record
One client below is named with their permission; the rest of the client work stays under NDA. Everything else here is disclosed under the bug-bounty programmes' own rules, so every line is checkable.
Team training
An intensive, on-site week of practical application-security training built for QA teams: the same manual, business-logic-first method the engagements use, taught by the person who wrote it.
Not sure it fits your team?
Ask about team trainingProcurement & trust
Need any of this signed or in writing? Request the paperwork
Pricing
Most security vendors hide their pricing so they can work out what you can afford. Here is mine.
€1,000
Every price below is days × this rate.
€2,000
Essential
€3,000
Standalone API
€4,000
Web application
€5,000
Mobile application
€2,000
Two days on one bounded target — a single new feature, user flow or endpoint group. Right before a launch, or as a first look ahead of a full engagement.
Not a full application test. A whole web app, API or mobile platform at multi-role depth is 3–5 days — see What I test.
€3,000
One full surface, tested across every role with the authorisation matrix fully exercised. You pick the surface; it is priced at that surface's own published rate, not a package markup.
A web or mobile engagement already covers the backend it exercises. Pick the standalone API engagement only when the API itself is the target, or when there is API surface your application never calls — that is sized on the scoping call.
€5,000
For teams shipping every week. A standing engagement where each release gets looked at, rather than one annual audit that is stale by March.
Questions
Forty-five minutes, no charge and no slide deck. You describe the application, who uses it and what would hurt most if it leaked; I ask enough questions to size the work honestly. You leave with a scope, a fixed price and a date. If penetration testing is not what you actually need yet, I will tell you that instead of selling you one.
Typically two to three weeks from a signed scope. Retainer clients get five working days' notice. If you have a hard deadline — a customer security review, a funding round, a certification audit — say so on the first call and I will tell you honestly whether it is possible.
For coverage, yes — running Burp's scanner across an application costs nothing and occasionally catches something. But no unvalidated scanner output ever reaches your report. Every finding is manually verified and manually exploited, because a finding you cannot reproduce is a finding your developers will ignore.
A findings report with reproduction steps, CVSS 4.0 scoring, business impact in plain language and a concrete fix for each issue. A one-page executive summary for non-technical stakeholders. A letter of attestation you can hand to customers and auditors. And a live debrief call with your engineers. You do not have to take my word for any of that — the complete sample engagement pack is downloadable above.
Yes, and it is inside the quoted price. One free retest of every reported finding, within 90 days of the report, with an updated attestation letter. The letter reflects what has been closed. Retainer clients are different: unlimited retests, no window.
A 30% non-refundable deposit on signature, with the balance due on delivery of the report, net 14 days. The deposit secures your slot — testing weeks are booked in advance and a held week that falls through cannot be refilled at short notice. Invoices are issued by The XSS Rat, VAT BE 0795 300 624, and reverse charge applies to VAT-registered businesses outside Belgium.
Always, before scoping begins. I will sign yours rather than insisting on mine. Client names are never disclosed without written permission — the public work you can see is bug bounty and VDP research, which is disclosed under those programmes' own rules.
Yes — professional indemnity and public liability, with certificates available on request during procurement.
I will explain every finding until your engineers are confident they understand it, and review fixes at retest. I do not take on remediation implementation itself: the person who tests the fix should not be the person who wrote it.
A test environment that mirrors production, credentials for every user role, any API documentation you have, and a named technical contact who can unblock access. Everything else is my problem.
No pitch deck. You describe the application, I tell you what testing it properly costs and how long it takes. If it is not worth doing, I will say so.
The call
45 minutes, no charge. You describe the application; I ask enough to size it honestly.
A fixed scope
Targets, roles, a fixed price and a fixed date, in writing, before anything starts.
The test
2–5 days by hand, then the report, a debrief and one free retest within 90 days.
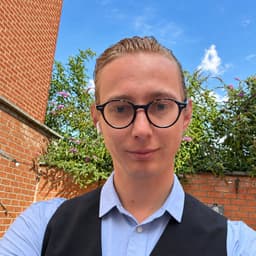
Wesley Thijs
You talk to the person who does the test.
 OpenAI, Google and Intigriti